Schedule a demo

Expert-led offensive cyber security

Assume they are already inside.

A breach in an estate your size is rarely dramatic. It is a dead subdomain, an unrotated supplier key, a password from a dump. We replicate the route, then show you exactly what it reaches.

Already across the industry

Our engineering team builds and runs systems for these organisations.

Avis
HNB
Hayleys
Federal Tax Authority
Qatar MCIT
Lake Nona
Shorelight
Nucleus Biologics
Ultimate Finance
CPL Group
NewWorld IGA
600+
Engineers
40,000
Merchants
1M+
Transactions monthly
24/7
Active monitoring

Capabilities

Two functions. One practice.

Everything we do is one of these. We attack your systems so you learn what an adversary reaches, and we watch them so you learn the moment one tries.

Offense

Attack my systems

You cannot defend what you have never seen attacked. We pursue an agreed objective the way a real adversary would, across people, process and technology, then show you every step we took.

  • Red teaming, covert or declared as a purple team
  • Black box testing from the outside in
  • White box testing, source assisted
  • Architecture review before the code exists
See how we engage →
Defense

Defend my systems

Most breaches are not clever, they are unwatched. We build the detection, then run it: a named analyst on every shift and a structured notification when something matters.

  • Active monitoring, every hour of every day
  • SIEM and EDR built, tuned and brought to coverage
  • Detection content mapped to real techniques
  • Escalation runbooks and analyst enablement
See how we engage →

Built by the same engineers. The people who write the detection spend their week evading it.

Who you are working with

We are not a testing boutique. We are the engineers who built the systems.

Surge runs payments for 40,000 merchants and products used by millions. When we test your platform we are testing something we have had to build, secure and keep running ourselves. That is why we know where the assumptions hide.

  • We run it in productionActive monitoring on live estates, not in a lab.
  • Same engineers, every roundSmall teams that stay on your account.
  • Named and reachableYour developers talk to whoever found it.

The gap

What you track is not what you expose.

Your register describes what you meant to build. Your attack surface is what you actually left running.

Exposure modelIllustrative
On your register0
Reachable from the internet0
Anything is watching0
208 reachable and unregistered · 362 reachable and unwatched

The debrief

Every red team ends in the same room.

We agree an objective with your board, pursue it as an adversary would, then replay the whole campaign beside your defenders.

Replay · objective: cardholder data store T+00:00Illustrative
T+00:00

Objective agreed

Crown jewel named, rules of engagement signed by your board.

Authorised
T+06:00

Reconnaissance

Staff, suppliers and stale infrastructure mapped from public sources.

No alert
T+1d 02:00

Initial access

One person in Finance entered credentials on a page we controlled.

Fired, not investigated
T+1d 09:00

Foothold

Access made persistent, surviving the controls meant to remove it.

No alert
T+2d 21:00

Lateral movement

Privileges escalated, then movement across the estate toward the objective.

Closed as false positive
T+3d 14:00

Objective reached

Cardholder data store opened. Nobody in the organisation raised a hand.

No alert
0
Days to objective
0
Detection opportunities
0
Alerts fired
0
Alerts investigated

How an engagement runs

Agreed in writing before anything is touched.

The same five steps whether we are attacking or defending. Nothing starts until the scope and the rules of engagement are signed by both sides.

01

Scoping

Assets, threat model and success criteria, agreed in writing.

02

Authorisation

Signed rules of engagement naming the assets, the window, the escalation contacts and the stop conditions.

03

Execution

Agents cover the ground. Every candidate is confirmed by an engineer before it reaches you.

04

Walkthrough

The written report, then an engineer taking your team through it line by line.

05

Retest

We verify your fixes once they land. Included, never billed separately.

Machine scale

  • Known vulnerabilities and stale components
  • Misconfiguration and exposed services
  • More of a codebase than a manual pass reaches

Engineer judgement

  • Authorisation flaws between two valid users
  • Business logic and state manipulation
  • Low findings chained into one critical path

What you get

The report is the product.

01

Short by design

A finding that takes a paragraph gets a paragraph. Nothing padded to justify a fee.

02

Coverage, not just findings

You see what was tested and what came back clean, not only what broke.

03

Every finding reproduced

Reproduced by an engineer and shipped with a working proof of concept.

04

Severity you can defend

Rated on exploitability and impact in your environment, not a generic score.

05

Publishable on request

A version written for your customers and auditors, with your sign-off on it.

06

Free retest

Once your fixes land we verify them. Included, never billed separately.

The way out

Request a red team.

Five questions. We will tell you honestly whether a red team is the right thing for you right now, and what we would run instead if it is not.

Step 1 of 5 · Your organisation
Your profile
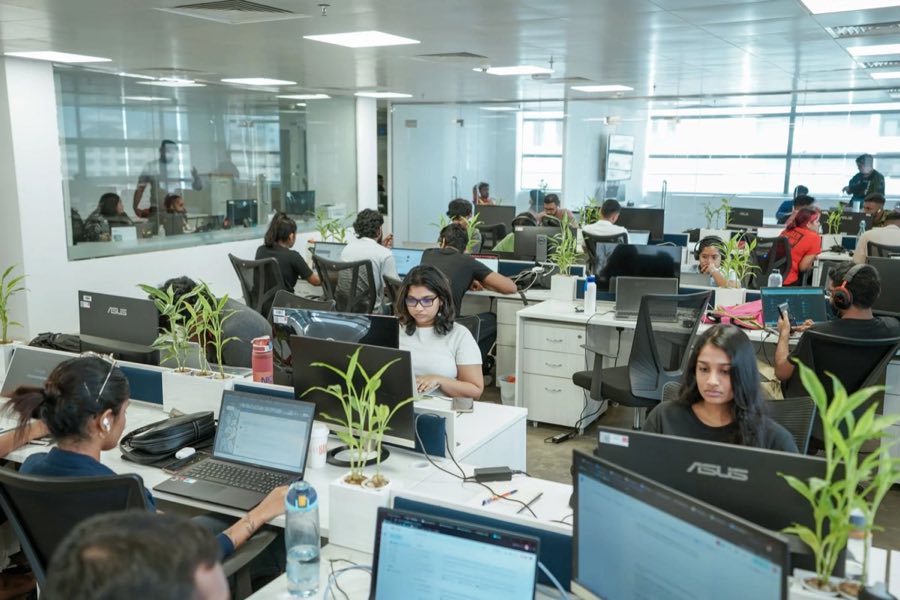
The Surge engineering floor in Colombo
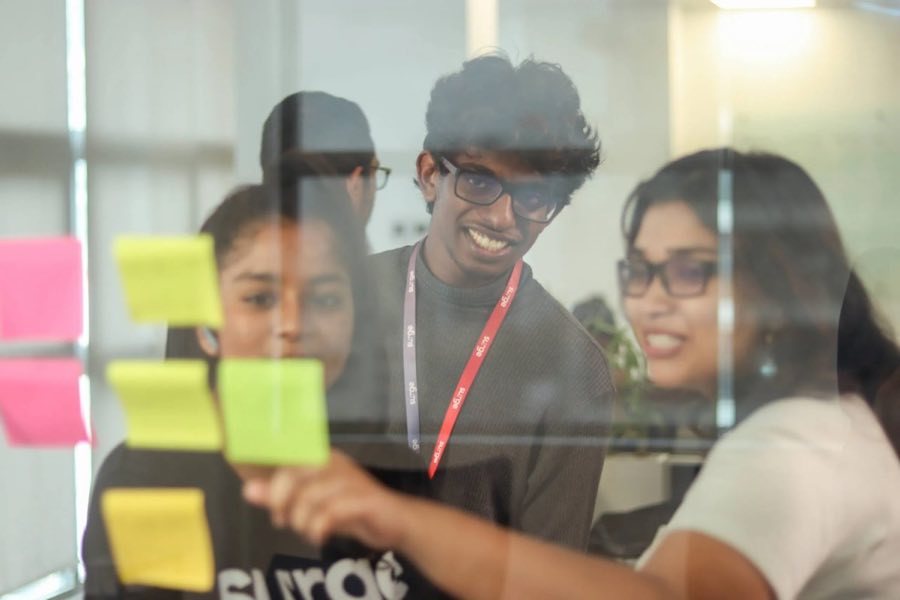
Surge engineers working through a problem at the glass wall
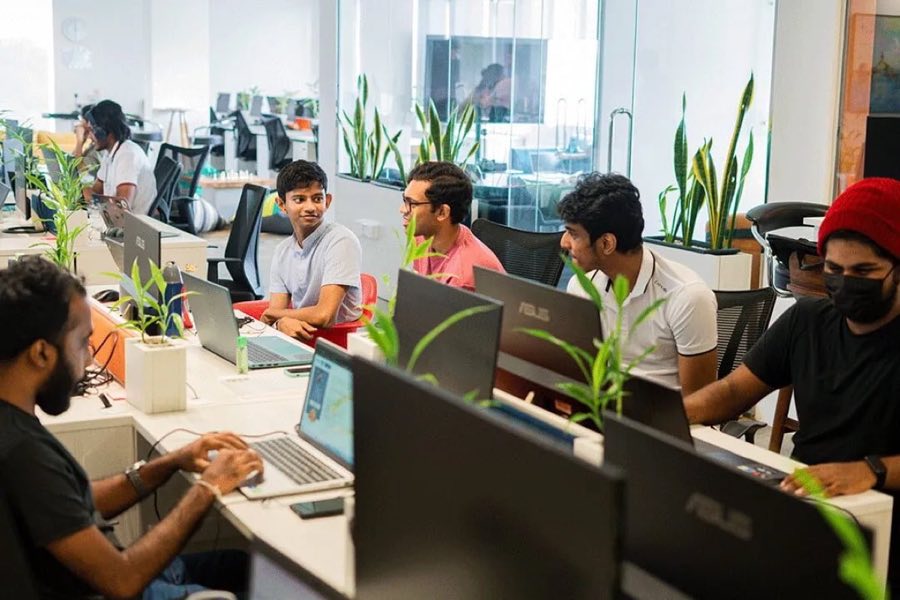
Surge engineers at their desks in Colombo
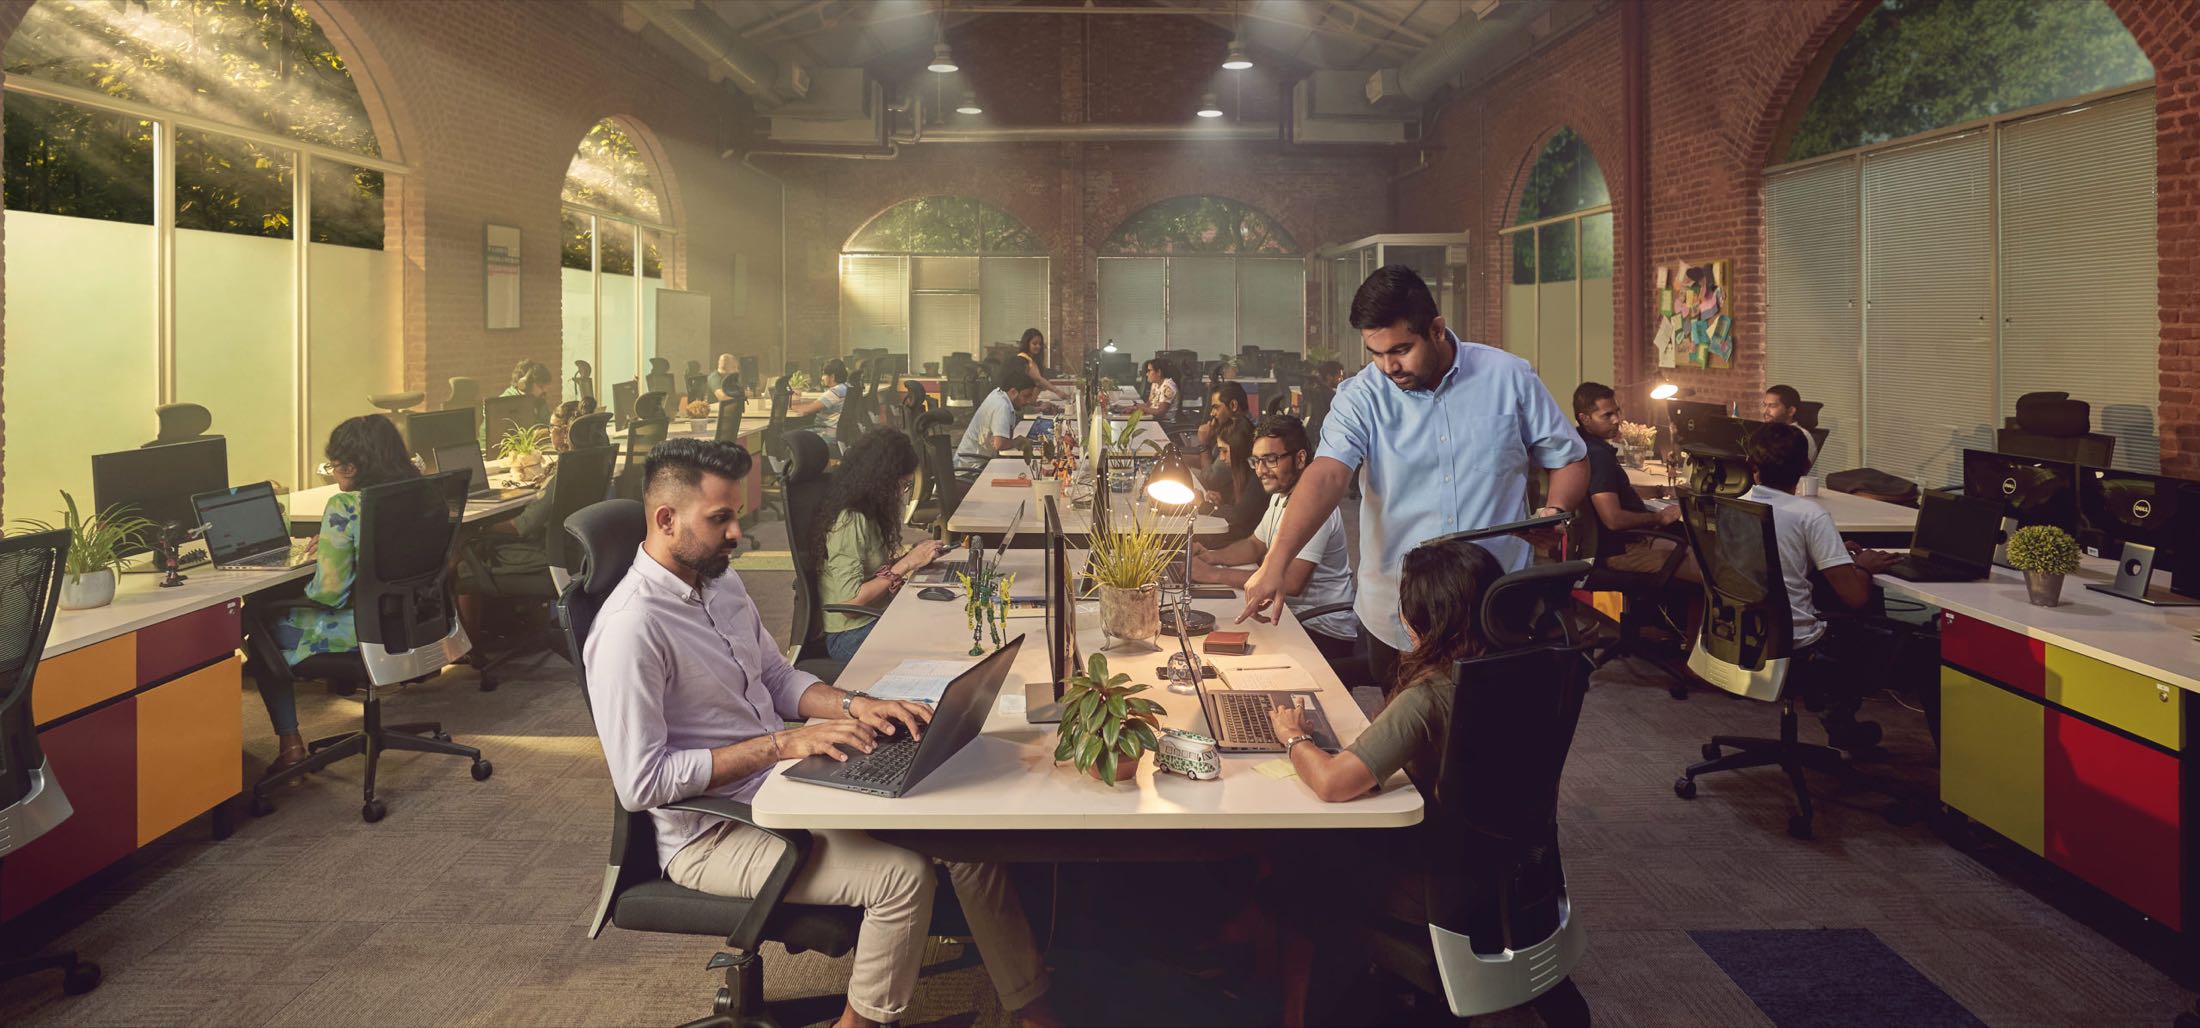
The Surge engineering floor, Colombo